Microsoft's Agent Framework package on PyPI is hijacked to steal cloud and CI credentials
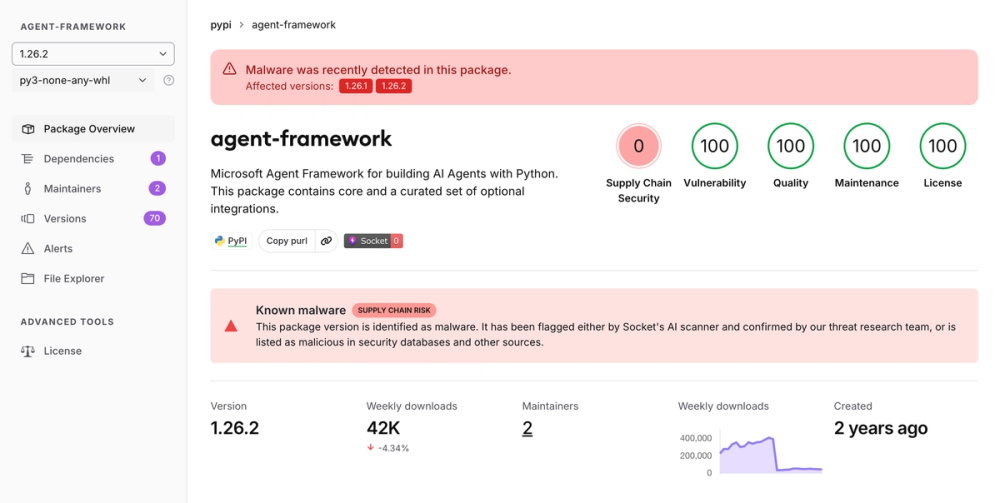
Versions 1.26.1 and 1.26.2 of agent-framework, uploaded on 17 November and since removed, ran a credential stealer on every Python start; how the attacker got publishing access is not known.
Why it matters
The attack hits the tooling developers use to build AI agents, and the payload targets exactly what agent pipelines hold: Azure managed-identity tokens, GitHub Actions OIDC tokens and CI secrets. Because it uses a .pth startup hook, it runs even if the package is never imported. Wiz says the malicious wheel did not match the project's normal release process, pointing to a direct upload. OX Security says it is the second Microsoft-related PyPI package compromised this year. Anyone who installed either version should remove it and rotate every credential the environment could reach.
Key facts
- Version 1.26.1 uploaded at 20:35 UTC on 17 November, 1.26.2 at 21:08 UTC
- Both gone from PyPI by 21:30 UTC, per Wiz
- The package gets about 41,000 downloads a week, per Wiz
- A .pth hook runs the stealer on every Python start
- Targets Azure, GitHub Actions OIDC and CI/CD credentials
- Root cause of the publishing access is unconfirmed